All Episodes
Displaying 141–157 of 157 in total
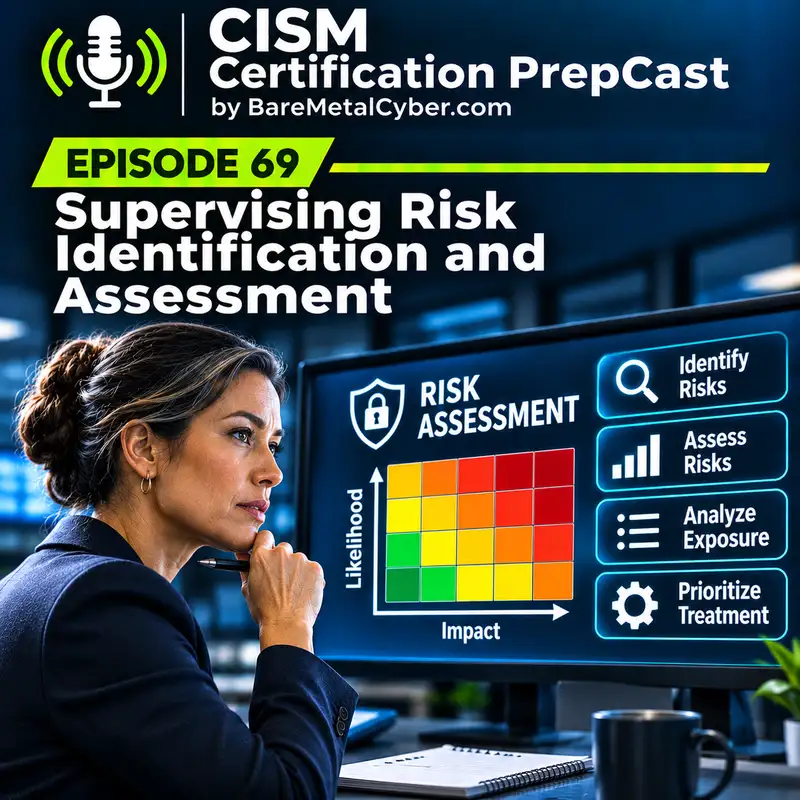
Supervising Risk Identification and Assessment
Supervising risk identification and assessment means ensuring that the method, scope, assumptions, participants, ownership, and outputs are appropriate for the decisio...
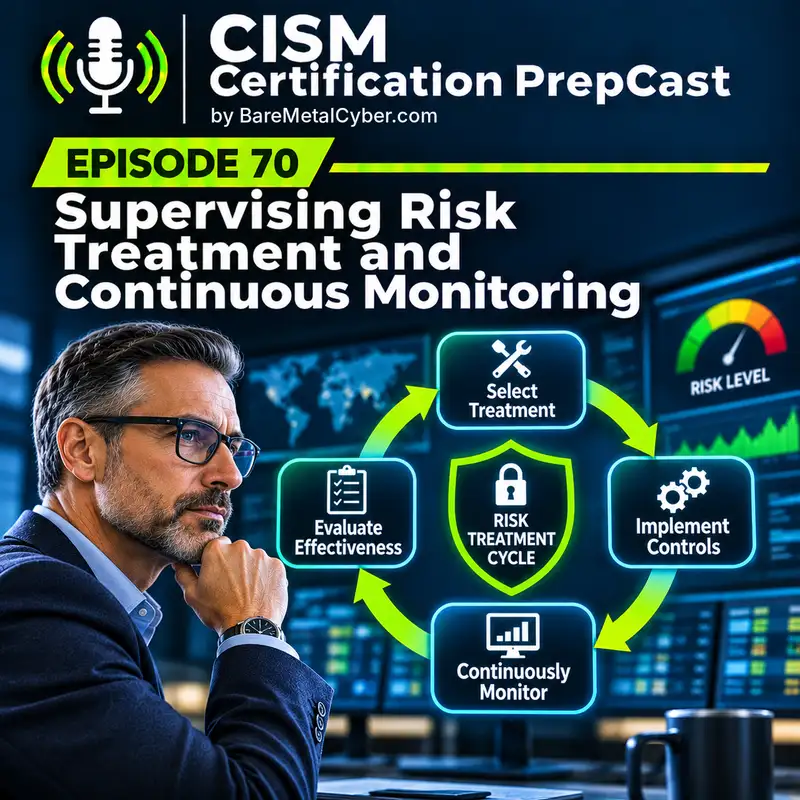
Supervising Risk Treatment and Continuous Monitoring
Supervising risk treatment and continuous monitoring ensures that approved decisions are implemented, observed, and reconsidered when conditions change. This episode e...
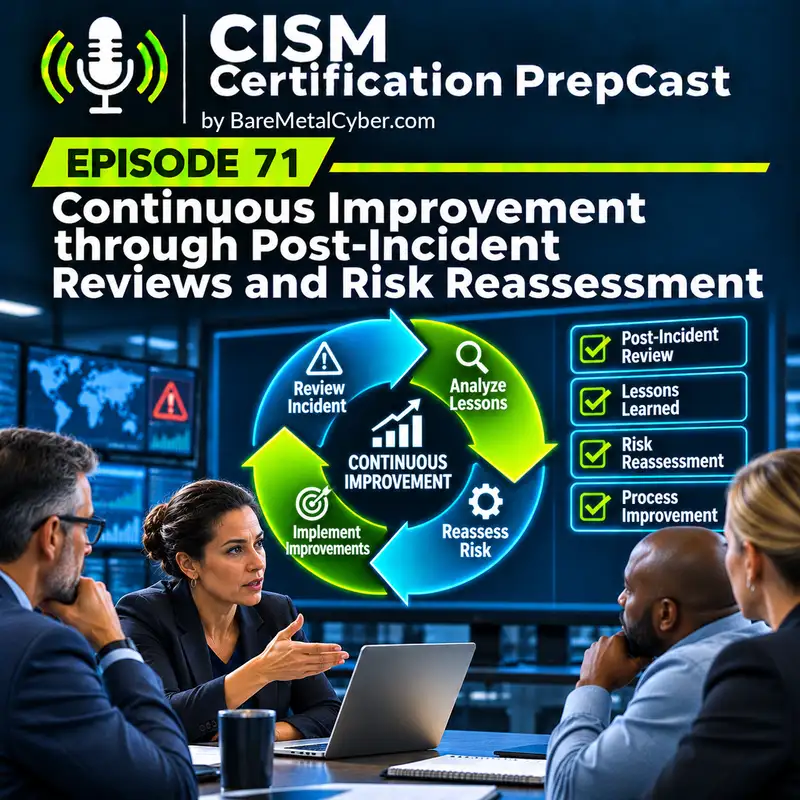
Continuous Improvement through Post-Incident Reviews and Risk Reassessment
Post-incident reviews and risk reassessment turn operational experience into changes that strengthen governance, architecture, controls, plans, funding, and readiness....
Making Security Decisions with Incomplete Information
Security managers frequently must act before every fact is known, but uncertainty does not justify either paralysis or unsupported confidence. This episode distinguish...
Enterprise Architecture Workshop: Current State to Target State
Enterprise architecture provides a structured way to understand how a business change affects capabilities, information, applications, technology, people, suppliers, a...
Information Security Architecture Workshop: From Risk to Control Evidence
Information security architecture translates risk decisions into requirements, trust boundaries, control patterns, integrations, and evidence. This workshop follows a ...
The CISM Decision Ladder in Action: Authority Under Pressure
The CISM decision ladder helps organize judgment through prioritize, authorize, communicate, and verify, but real situations do not always unfold in a neat sequence. T...
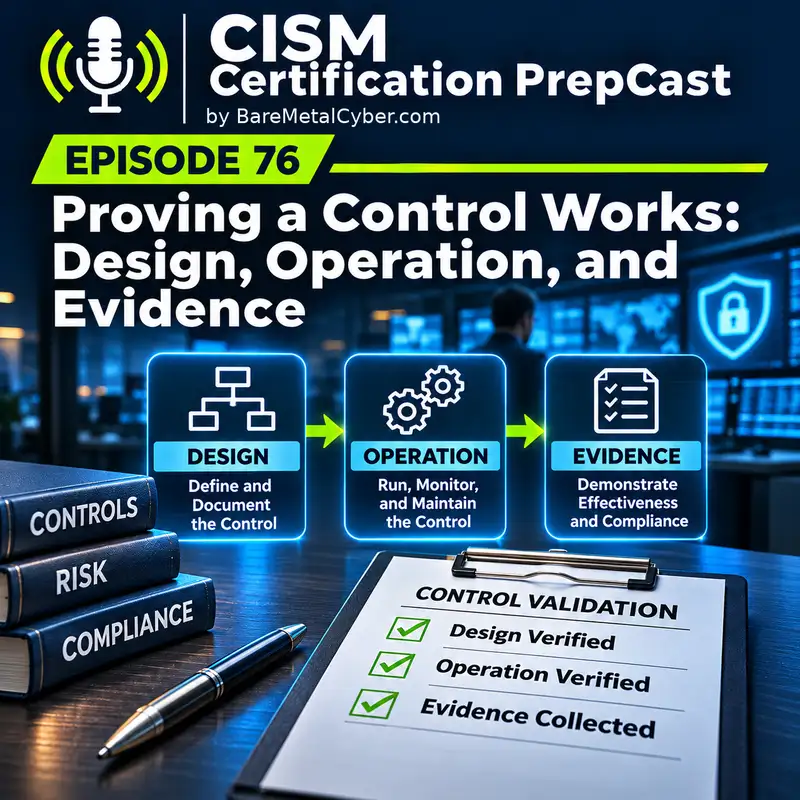
Proving a Control Works: Design, Operation, and Evidence
A claim that a control works must be supported by evidence about its design, implementation, operation, coverage, and limitations. This episode follows a control-effec...
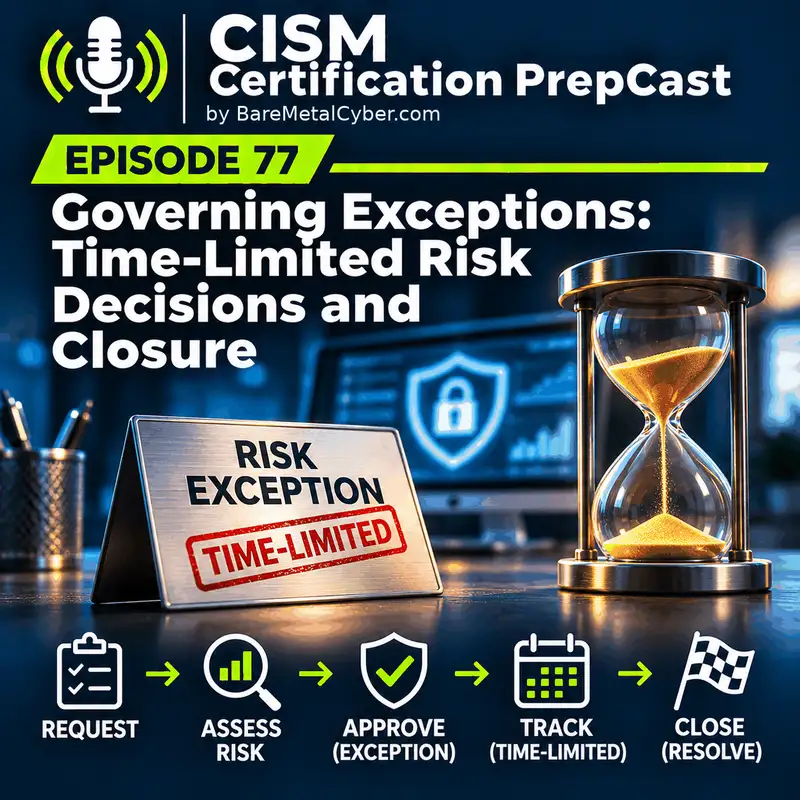
Governing Exceptions: Time-Limited Risk Decisions and Closure
Security exceptions permit a defined deviation from an approved requirement, but they must remain time-limited, owned, monitored, and subject to closure. This episode ...
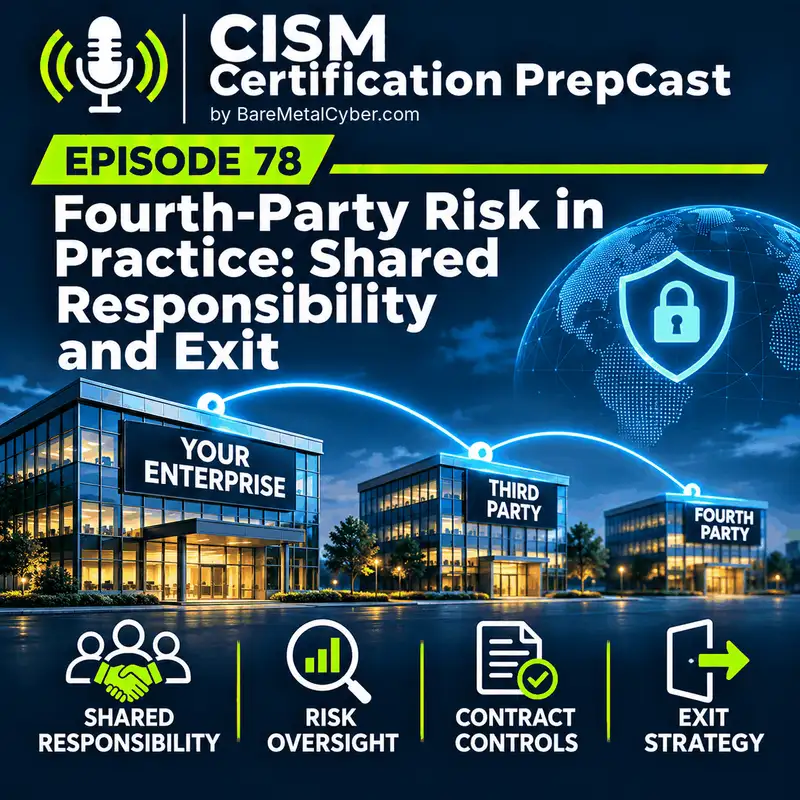
Fourth-Party Risk in Practice: Shared Responsibility and Exit
Fourth-party risk appears when a directly contracted supplier depends on other providers that also influence the security and continuity of the service. This episode f...
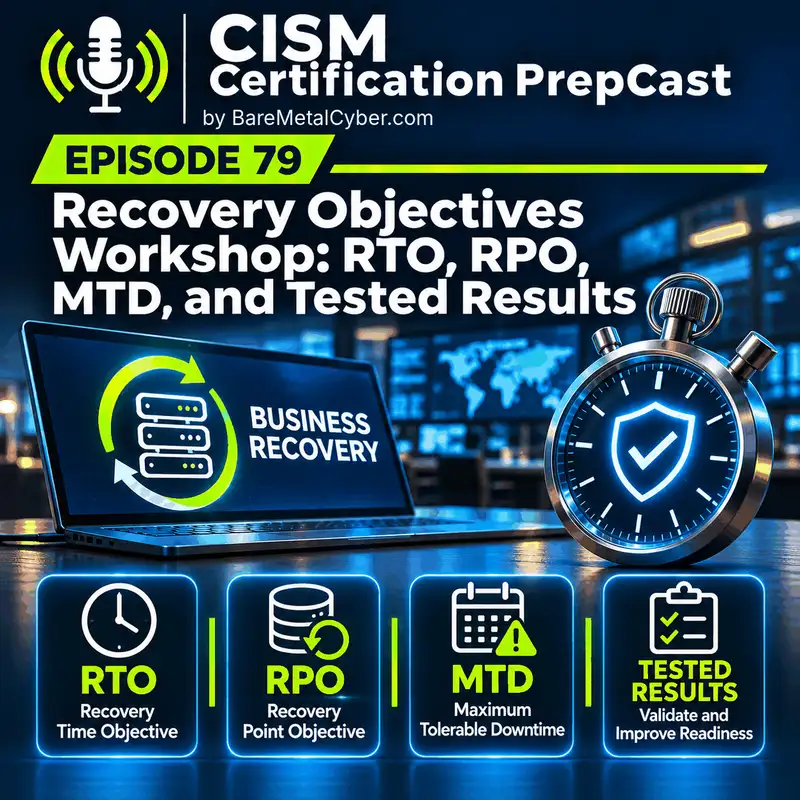
Recovery Objectives Workshop: RTO, RPO, MTD, and Tested Results
Recovery objectives answer different questions and must not be combined into one generic measure of downtime. This workshop explains recovery time objective, recovery ...
Containment Decisions: Limiting Harm Without Creating a Larger Outage
Containment decisions must reduce immediate harm without unnecessarily damaging a larger business service or destroying important evidence. This episode compares sever...
Return-to-Service Decisions: When Recovery Is Safe Enough to Authorize
Returning a service to operation is an authorized risk decision, not merely a technical declaration that systems are running. This episode follows recovery after conta...
Metrics That Change Decisions: From Dashboard Activity to Business Outcomes
A reassuring dashboard can still fail to answer the decision that leadership actually faces. This episode examines how counts, percentages, averages, and trends can hi...
Emerging-Risk Workshop: From AI Proposal to an Accountable Decision
An artificial intelligence proposal becomes manageable when the organization defines the business use, data, model behavior, suppliers, decisions, obligations, and con...
Tabletop to Verified Improvement: Designing an Exercise That Changes Readiness
A tabletop exercise creates value only when it tests a defined capability and its findings lead to verified improvement. This episode follows an exercise from objectiv...
CISM Management Capstone: From Strategy to Incident and Back
The CISM management capstone integrates governance, risk management, security program development, and incident management across the lifecycle of one fictional busine...