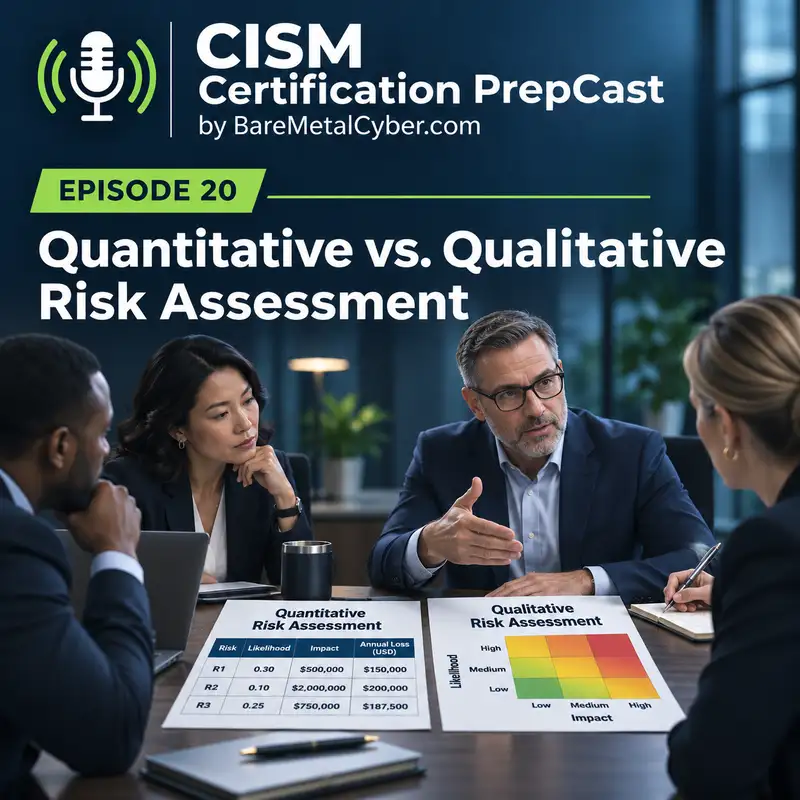
Quantitative vs. Qualitative Risk Assessment
In this episode, we are examining quantitative and qualitative risk assessment. Qualitative and quantitative methods are tools for decision support. Neither method is automatically mature, objective, or correct. Quality depends on the risk scenario, data, assumptions, definitions, and the decision the assessment must support.
A fictional logistics company must decide whether to redesign a booking service, purchase additional insurance, or accept temporary exposure. Some loss data exists, but significant uncertainty remains. The manager needs a method that communicates the range of possible outcomes without presenting guesses as facts.
Risk assessment is one of the most fundamental responsibilities of a security leader. It provides a systematic way to identify and prioritize threats to the organization's information assets. Without risk assessment, security decisions may be based on assumptions or personal opinions rather than actual exposure. A well-conducted assessment supports informed decision-making. It guides which risks to mitigate, which controls to implement, and which areas require the most attention.
Beyond operational value, risk assessment plays a strategic role. It helps align security initiatives with the organization's broader business goals and risk tolerance. The results form the basis of governance reporting, compliance documentation, and risk treatment planning. Over time, risk assessment results inform budget justification, control performance reviews, and updates to security policies. It is not a one-time activity but an ongoing function embedded into the governance lifecycle.
Risk assessments can be conducted using qualitative or quantitative methods. Qualitative risk assessment is based on descriptive scales, typically high, medium, or low, for likelihood and impact. This approach uses interviews, facilitated workshops, and expert judgment to evaluate threats and vulnerabilities. It does not require numeric data, which makes it well-suited for organizations without mature data analytics capabilities. It provides a conceptual view of exposure and is often the first step in understanding a risk environment.
Qualitative methods are commonly used in environments where data is scarce, incomplete, or too difficult to validate. They are relatively quick to perform and can cover a wide scope with minimal resources. Another strength of qualitative risk assessments is that they are easy to communicate. Since results are presented in everyday language, they can be shared with both technical teams and non-technical executives. This makes qualitative assessments highly effective for starting conversations and building consensus.
Quantitative risk assessments take a more data-driven approach. They assign numeric values to both likelihood and impact. These values can then be used to calculate metrics such as Annualized Loss Expectancy, or ALE. Quantitative methods rely on statistical models, historical incident data, or simulated threat scenarios. They require more time and effort to complete but offer more precise and defensible results. They allow leaders to understand risk in terms of dollars, downtime, or other measurable outcomes.
This numerical approach supports cost-benefit analysis. By calculating potential losses, organizations can compare the cost of controls against the risk they reduce. Quantitative assessments also support more advanced modeling. Probability distributions, decision trees, and Monte Carlo simulations can be used to reflect uncertainty and variability. This allows security leaders to run what-if scenarios, prioritize investments, and communicate in financial terms that resonate with business stakeholders.
Qualitative methods have several strengths that explain their continued use. They are simple to implement, do not require specialized tools, and can be applied to any business unit or risk domain. They are especially useful during early-stage assessments or when exploring new areas such as emerging technologies or untested third parties. They allow for broader stakeholder involvement because participants do not need technical knowledge or risk analytics training.
When expert consensus is available but reliable data is not, qualitative assessments help translate collective experience into structured insights. These assessments also support custom scoring models. Organizations can tailor their scales, criteria, and weighting to match their unique needs. This flexibility helps security teams reflect their operational realities and align the process with organizational culture.
Quantitative risk assessments offer advantages that go beyond simplicity. Because they use validated data and defined formulas, their results are often considered more objective and defensible. This is especially important when risk results must be presented to auditors, regulators, or financial officers. These methods also support justification of investments. Security leaders can explain that a particular control will reduce expected loss by a specific amount, improving the ability to secure funding.
Quantitative models can incorporate probability, uncertainty, and interdependencies, features that improve realism and accuracy. These methods align well with enterprise risk management frameworks, which often require financial impact estimates and standardized comparisons. By using consistent units of measurement, organizations can compare cyber risk alongside operational, financial, or reputational risk. This integrated view improves decision-making at the executive level.
Still, each method has limitations. Qualitative risk assessments rely on subjective scales. What one team considers "high impact," another might call "moderate." These terms are open to interpretation, and application may vary by region, business unit, or assessor. This inconsistency makes it difficult to compare results across teams or over time. Without financial values, it is hard to quantify potential loss or return on investment.
Qualitative assessments also struggle to meet audit or regulatory expectations when precision is required. In complex environments, risk registers may contain hundreds of qualitative entries that cannot be aggregated into a meaningful enterprise risk score. While useful as a first step, qualitative results must often be supplemented with deeper analysis to guide strategic planning or budgeting.
Quantitative assessments have their own drawbacks. The most significant is the requirement for high-quality data. If data is outdated, incomplete, or inaccurate, the results of the assessment may be misleading. Complex models can also be difficult to build correctly. They may introduce errors, assume false precision, or obscure important assumptions. Not every risk can be quantified. Human behavior, geopolitical instability, or technology disruption often resist measurement.
Building and maintaining a quantitative model takes time, resources, and ongoing effort. Organizations must also train their teams to interpret the results. Executives may be unfamiliar with probability distributions or simulation outputs, which can lead to misunderstanding. Security leaders must be able to explain what the numbers mean, how they were derived, and what actions are recommended.
Choosing the right approach for your organization requires alignment with maturity level, available data, and decision-making needs. If the organization is early in its security journey, or if data is scarce, a qualitative approach may be best. If leadership is focused on speed, flexibility, and broad participation, qualitative methods provide a faster path to risk insights. However, for high-value assets, regulatory decisions, or mission-critical systems, quantitative methods may be necessary.
Many organizations adopt hybrid approaches. They use qualitative methods to assess risk broadly and then apply quantitative methods to selected high-risk areas. This balance offers depth where it is needed and speed where it is not. Regardless of the method chosen, the rationale should be documented. Governance bodies, auditors, and stakeholders should understand why a certain method was used and how it aligns with the organization's objectives.
Transitioning from qualitative to quantitative analysis is possible, but it takes planning. Start by improving data collection. Identify which variables, such as asset value, incident frequency, or control effectiveness, can be measured consistently. Improve asset inventories and ensure threat intelligence is reliable. Refine inputs gradually over time. Introduce analytics tools such as Monte Carlo simulations or decision tree models to bring in probabilistic reasoning.
Training is essential. Stakeholders need to understand how to interpret and act on the outputs of quantitative models. This includes understanding the assumptions and limitations behind each figure. Establish consistent units of measurement across departments. This may include using financial impact as a common metric, or defining time-based impact scales. As these practices mature, your organization will gain confidence in using quantitative analysis for both strategic and tactical decisions.
Whether using qualitative, quantitative, or hybrid methods, risk assessments must be fully integrated into enterprise risk management. Assessment results should directly inform risk treatment plans, program priorities, and investment decisions. Reporting formats should be standardized to allow presentation to executives, boards, and regulators. Results should be aligned with other governance functions and rolled into broader enterprise risk posture reviews.
As new threats emerge or incident patterns change, assessment models must be updated. New technologies, business lines, or compliance requirements may alter both likelihood and impact values. This makes risk assessment an iterative process, not something to complete once and forget. It must be embedded into operational reviews, budget planning, and policy updates. By making assessment part of the security program's rhythm, organizations improve accuracy, responsiveness, and relevance.
Asset value only becomes useful in risk assessment when it is expressed in terms the business already uses to make decisions. A server, application, database, or third-party service is not valuable because it exists, but because it enables revenue, operations, trust, safety, or compliance. In exam scenarios, the fastest way to "translate" asset value is to name the dependent business process and the consequence of that process failing. When the question stem gives you a business context, treat it as a clue about what the organization truly values, not as narrative decoration.
Use the architecture view to set scenario boundaries. Include the information flow, shared identity service and external provider on which the business depends. A failure in one shared component may affect several services and change the assessed impact.
A common mistake is treating asset value as a fixed dollar amount, as if the organization has a universal price tag for every system. In practice, value is situational and changes based on timing, dependencies, and stakeholders, and the exam rewards answers that recognize this. A payroll system may be "routine" most days, but it becomes mission critical near payroll cutoff, during a merger, or when regulatory scrutiny is heightened. Value is also shaped by concentration of sensitive data, especially where aggregation increases the blast radius of a single compromise. Thinking in terms of "what business capability is lost" will almost always outperform thinking in terms of "what technology is affected."
Impact types are the bridge between asset value and the reason a risk is managed at all. Many organizations use the confidentiality, integrity, and availability (CIA) triad as a mental model, but executive decision-making often lands on financial, operational, legal and regulatory, safety, and reputational outcomes. Those are not competing perspectives; they are different ways of describing the same harm in the language of different audiences. A data integrity failure might be described technically as unauthorized modification, but the business impact is defective reporting, wrong decisions, or incorrect customer billing. In exam logic, the "best answer" usually connects the technical event to a business impact category with minimal leaps.
Confidentiality impact is easiest to oversimplify because it often gets reduced to "data was stolen" without identifying why that matters. The business language of confidentiality is typically framed as loss of customer trust, loss of competitive advantage, breach notification obligations, contractual penalties, or increased fraud. Executives also understand confidentiality in terms of who else can make money from your information, or how a disclosure changes negotiating position in a market. When the scenario mentions intellectual property, strategic plans, or product roadmaps, confidentiality is often the primary impact even if systems remain fully available. When the scenario mentions regulated personal data, confidentiality tends to pull legal and reputational impacts into the foreground.
Integrity impact is frequently underweighted because it does not always produce a visible "incident" in the way an outage does. In business terms, integrity failures create decisions made on bad information, financial misstatements, defective products, safety incidents, and operational rework that quietly drains capacity. A manipulated configuration baseline, altered access control rule, or poisoned dataset is an integrity risk even if nothing is exfiltrated. Executives care about integrity when the organization must stand behind accuracy, such as financial reporting, clinical results, industrial controls, or audit evidence. For exam questions, integrity is often the best answer when the stem emphasizes correctness, trustworthiness, or assurance rather than secrecy.
Availability impact maps cleanly to business continuity, but it should not be treated as "downtime equals bad" without context. The business language here is missed revenue, halted operations, service level agreement penalties, customer churn, and safety exposure when systems support life or critical processes. Availability is also about the organization's ability to deliver at the required time, which is why peak periods and deadlines matter. A four-hour outage might be tolerable for a back-office tool, yet catastrophic for an online ordering platform during a holiday surge. In exam scenarios, look for hints about time sensitivity and operational dependency to calibrate the true impact.
Reputational impact deserves careful handling because it is real but often poorly defined, and the exam typically prefers answers grounded in measurable consequences. Reputation matters because it drives customer behavior, partner confidence, investor reaction, and regulator posture, but it is easiest to misuse as a vague catch-all. Strong risk assessment language ties reputational harm to a specific stakeholder reaction, such as lost renewals, increased acquisition costs, or diminished willingness of partners to share data. Reputational impact also compounds other impacts by increasing the cost and duration of recovery efforts. When a scenario includes public visibility, brand promises, or trust-based services, reputational impact becomes a first-class factor rather than an afterthought.
Financial impact is not limited to immediate incident response expenses and should not be treated as synonymous with "the cost of a breach." In risk assessment, financial impact includes lost revenue, productivity loss, legal fees, regulatory fines where applicable, settlement costs, and longer-term investments required to restore control confidence. It can also include opportunity cost, such as delaying product launches or abandoning markets because risk tolerance is exceeded. Many organizations think in ranges rather than single numbers because the point is comparability, not accounting precision. On the exam, the financially grounded answer is usually the one that links a technical event to a business outcome the organization would recognize on a dashboard.
Legal and regulatory impact is best expressed as obligations and constraints rather than fear of punishment. In business language, this impact type includes breach notification duties, audit findings, license restrictions, contractual noncompliance, and enforcement actions that change how the organization can operate. The key is that legal exposure often persists after systems are restored, creating a long tail that executives will prioritize. A risk assessment that ignores legal requirements tends to underestimate impact, especially where data residency, critical infrastructure rules, or sector regulations are involved. In exam reasoning, legal and regulatory impact often outweighs technical convenience because it affects the organization's permission to do business.
The management skill in risk assessment is choosing the language that enables action without distorting the underlying reality. Technical teams need specificity about what failed and how, while leaders need clarity about what is at stake and what tradeoff is being proposed. A well-framed statement of impact can be evaluated, funded, and tracked, whereas jargon-heavy descriptions often turn risk into a debate about terminology instead of a decision about exposure. The best practice, and the exam-friendly approach, is to express asset value through the business process it supports and to describe impacts in categories that match executive priorities. When you can move cleanly from "asset and dependency" to "impact type and business consequence," you are doing risk assessment as a management process rather than as a paperwork exercise.
Impact alone does not complete the analysis. Likelihood must be reasoned from threat capability, opportunity, exposure, control performance, and uncertainty rather than from an unsupported label.
Likelihood estimates should match the evidence and the decision. Both qualitative and quantitative approaches can be useful when the scenario, timeframe, assumptions and uncertainty are explicit. A precise-looking percentage is weak if nobody can explain its basis; a numerical estimate supported by relevant data can improve comparison and investment decisions. The same discipline applies to labels such as "high" or "unlikely." The goal is to make a reasoned estimate that supports action and can be reviewed as evidence changes.
A practical way to reason about likelihood is to separate "how exposed are we" from "how capable is the threat" and then ask what has to go wrong for loss to occur. Exposure is shaped by how the asset is connected, who can access it, what control gaps exist, and how quickly those gaps are detected. Threat capability is shaped by motivation, resources, and opportunity, which vary dramatically across scenarios and attacker types. When the stem describes an internet-facing system with weak authentication and no monitoring, likelihood should rise even if the organization has never had a documented incident. When the stem describes a segmented system with strong access controls and tight change management, likelihood can reasonably be lower even if the impact would be severe.
Frequency and probability describe different things. Frequency concerns the number of occurrences over a period; probability concerns the chance of a defined event or outcome, within a stated period when relevant. Define whether your estimate concerns a threat event occurring, its success, or the resulting harm, and keep the basis consistent when comparing scenarios. Frequent minor events and rare severe events may both deserve attention. Likelihood changes as exposure, controls, architecture and threat conditions change. A useful assessment explains these dependencies instead of treating likelihood as a fixed property of the asset.
Evidence for likelihood does not have to be perfect to be useful, but it does need to be honest about its limits. Incident history is relevant, yet it is also biased by detection capability, reporting culture, and how long the environment has been stable. Vulnerability and configuration data provides concrete indicators of exposure, but it can mislead if it ignores compensating controls or actual exploitability. Threat intelligence can improve context, but it should be applied as "this actor targets environments like ours" rather than as a promise that an attack will happen next week. The strongest likelihood rationale blends multiple indicators and remains explicit about uncertainty instead of hiding it behind a precise-looking score.
Control strength is often the deciding factor in likelihood reasoning, but it must be evaluated as operated, not as documented. A policy that requires patching within thirty days is not a control if the organization regularly misses the window and has no exception process. Monitoring that produces alerts is not effective if the alerts are ignored or cannot be investigated due to staffing constraints. Likelihood should increase when controls are inconsistent, incomplete, or bypassable, even if they look good in a spreadsheet. In exam terms, a governance-oriented answer will focus on whether controls are implemented and operating as intended, because that is what changes the probability of loss.
Time is an underused lens for likelihood, and it is often the subtle clue that separates a good answer from the best answer. A vulnerability with a publicly available exploit, active scanning, and no compensating control increases likelihood sharply over a short horizon. A dependency on a third-party service with unclear change notification practices may create a slower-moving likelihood profile, but one that grows as integrations expand. Likelihood also shifts after major events like acquisitions, rapid cloud migrations, or restructuring, because changes create temporary windows where controls and asset inventories lag reality. When a scenario emphasizes rapid change, treat it as a likelihood amplifier unless the organization has demonstrated mature change control and validation.
Avoiding false precision does not mean avoiding structure. A qualitative approach uses defined descriptive levels, such as low, medium and high. A semi-quantitative approach uses scoring scales or bands to compare risk, but those scores are not automatically monetary values or probabilities. A quantitative approach uses numerical estimates with a meaningful scale, such as expected loss frequency or financial impact. Choose the approach that fits the available evidence and decision. In every case, document assumptions, use consistent criteria and explain uncertainty so another assessor can follow the reasoning.
For a simplified example, assume an estimated loss-event frequency of zero point two per year and an average loss of five hundred thousand dollars per event. Multiplying them gives expected annual loss of one hundred thousand dollars. These illustrative estimates support comparison; they do not predict a loss of one hundred thousand dollars next year. Test how the result changes with different frequency and impact assumptions, and consider whether a plausible severe event would exceed tolerance even when its expected annual loss looks affordable.
Scenario-based thinking is the most exam-relevant way to demonstrate likelihood reasoning without pretending you can predict the future. Imagine a cloud-admin credential exposed through poor identity lifecycle practices, where multifactor authentication is inconsistent and privileged sessions are not monitored. The likelihood of misuse rises because the threat does not need sophistication, only opportunity, and the pathway to impact is short. Now imagine the same credential exposure where privileged access management is enforced, conditional access blocks risky sign-ins, and anomalous privileged actions trigger rapid response. The likelihood of successful exploitation falls, not because the threat disappears, but because the conditions for success are constrained.
The managerial outcome of good likelihood reasoning is a prioritized set of risks that leaders can actually act on, with clarity about what would lower likelihood in the next cycle. When likelihood is framed as a reasoned estimate, it becomes easier to justify investments in prevention, detection, and response because you can explain which conditions are being improved. This approach also supports reassessment because you can revisit the same indicators after a control change and see whether the rationale still holds. The exam's "best answer" logic consistently favors this transparency: acknowledge uncertainty, ground likelihood in observable conditions, and describe how management decisions can change the odds. That is how likelihood becomes a tool for governance rather than a ritual of precision.
Qualitative analysis may be best when speed and limited data require structured judgment. Quantitative analysis may be best when reliable inputs and financial decisions justify deeper modeling. A hybrid approach can screen broadly and analyze selected material scenarios in greater detail.
For practice, assess one fictional risk both ways. Create a qualitative rating with defined criteria, then build a simple quantitative range with explicit assumptions. Compare what each method reveals and where each could mislead.