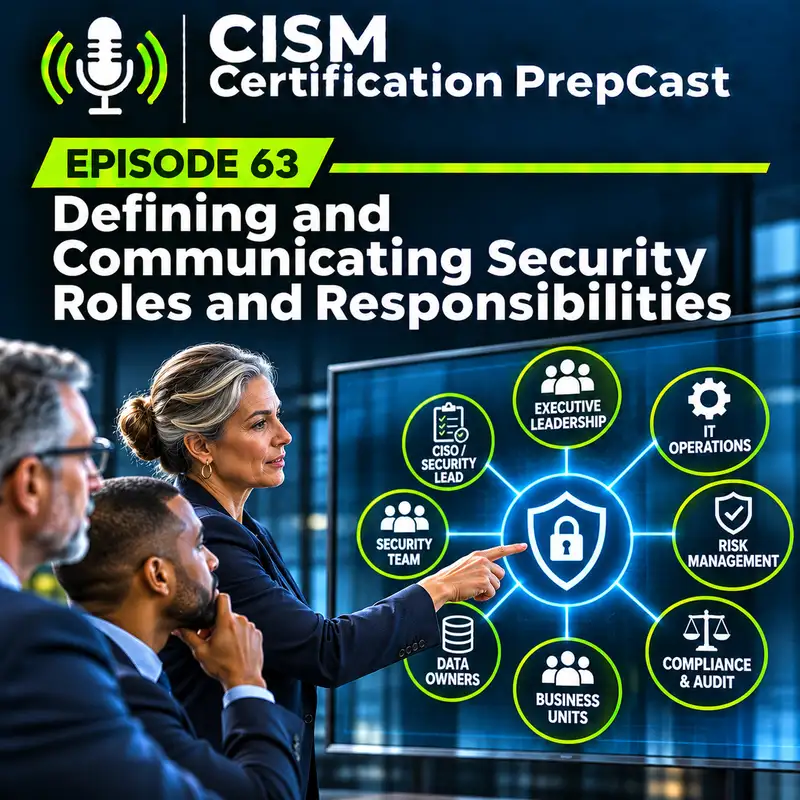
Defining and Communicating Security Roles and Responsibilities
Security roles are effective when people understand not only their tasks but also their decision rights, accountability, escalation paths, and communication obligations. This episode distinguishes governance, management, operational, risk, control, service, incident, and support…
CURRENT EDITION: CISM 2026. This episode is part of Season 2, the recommended course for the current certification exam.
Security roles are effective when people understand not only their tasks but also their decision rights, accountability, escalation paths, and communication obligations. This episode distinguishes governance, management, operational, risk, control, service, incident, and support responsibilities. It explains delegation, segregation of duties, RACI models, authority limits, risk acceptance, documentation, onboarding, and performance review. The discussion also covers organizational changes and third-party roles. Learners gain a practical way to prevent overlap, gaps, and delayed action by making responsibility visible and testable. Visit BareMetalCyber.com for more cybersecurity education, certification preparation, and practical security management guidance.